By using large language models to compare software code before and after an update, attackers are shrinking the window for organisations to patch known flaws
Back to Business
Business
November 17, 2026 at 5:36 AM
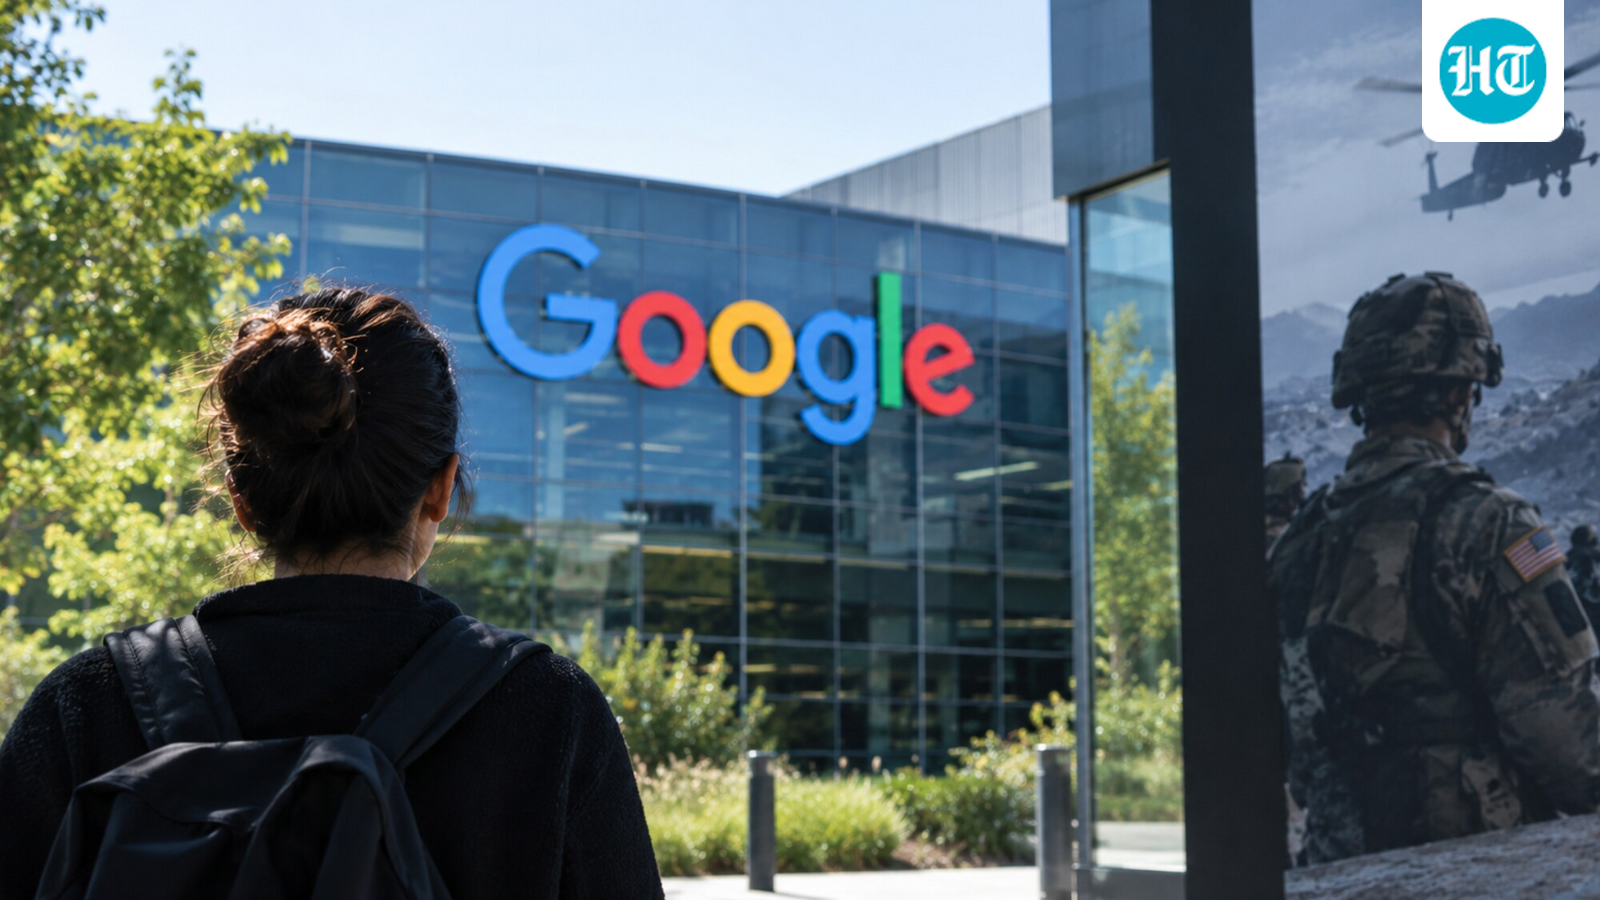
Threat actors using AI to mount cyberattacks, often without human help: Google
Hindustan Times Business
Excerpt from Hindustan Times Business.